

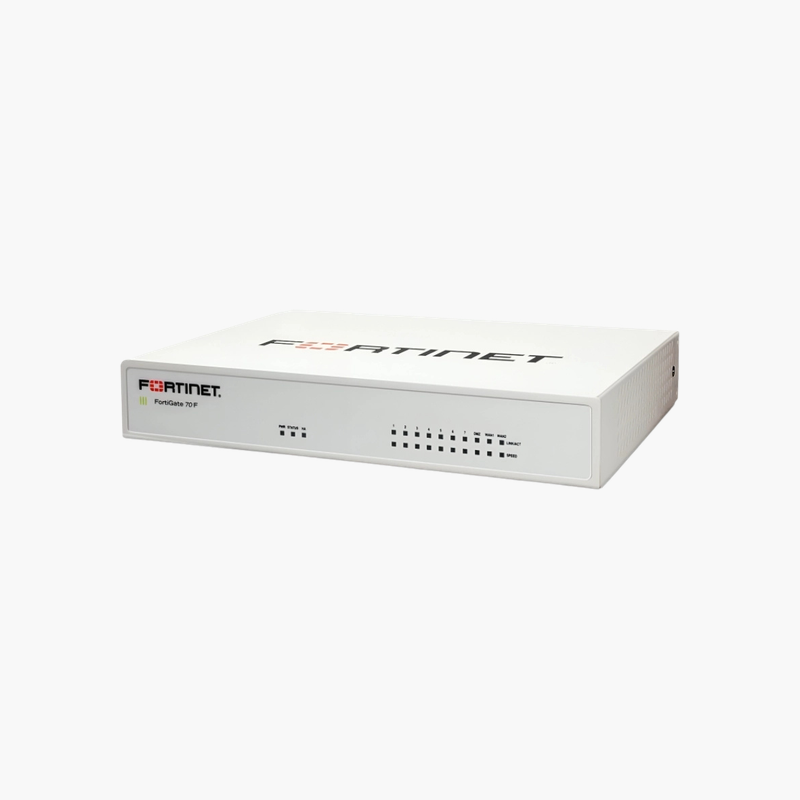
Next-generation firewall and Secure SD-WAN for small and mid-sized offices and distributed branches.
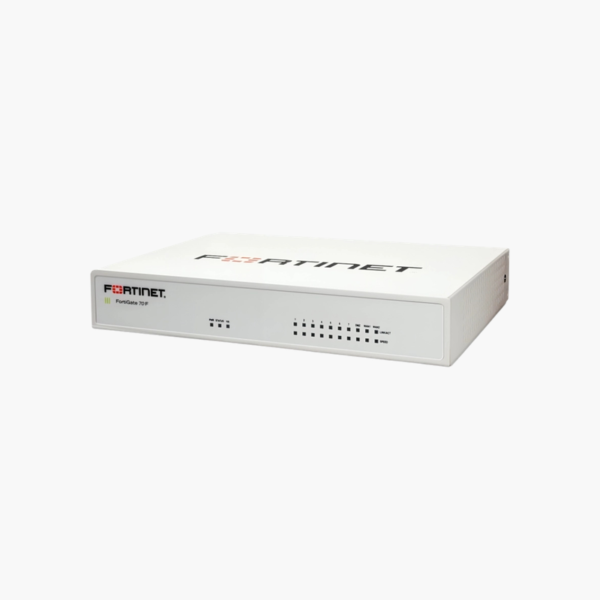
The Fortinet FortiGate 61F (FG-61F) is a desktop next-generation firewall that combines threat protection, Secure SD-WAN and IPsec VPN on FortiOS. With 10 Gbps firewall and 700 Mbps threat protection throughput, it suits small and mid-sized offices and distributed branches.
Why Basic Routers and Legacy Firewalls Leave Networks Exposed
Most attacks now arrive inside encrypted web traffic, cloud applications and phishing links. A basic router with port filtering cannot see any of that, and older firewalls slow to a crawl when IPS and antivirus inspection are switched on, forcing teams to choose between security and speed.
The FortiGate 61F uses Fortinet’s purpose-built security processors to inspect traffic in hardware. That is why it can sustain 1.4 Gbps of IPS and 700 Mbps of full threat protection (IPS, antivirus, application control) while still forwarding 10 Gbps of firewall traffic.
FortiOS also includes Secure SD-WAN at no extra cost: the firewall measures latency, jitter and packet loss on each internet link and routes applications like Microsoft 365 or VoIP over the best path. Branches connect back to head office with 6.5 Gbps of IPsec VPN throughput.
Security Fabric Integration
The FortiGate 61F is the hub of the Fortinet Security Fabric. Through FortiLink it manages FortiSwitch switches and FortiAP access points from the same FortiOS console, and it shares threat intelligence with FortiAnalyzer, FortiClient and FortiSandbox for coordinated response.
128 GB SSD Local Storage for Logging and Reporting
The built-in 128 GB SSD stores traffic, threat and event logs on the appliance, so FortiView dashboards and reports are available without an external log server. This helps smaller IT teams meet audit and compliance requirements.
How to Set Up the Fortinet FortiGate 61F
- Place the appliance on a desk or mount it in a rack, connect power, and connect your internet link to a WAN port.
- Connect a PC to an internal port, open https://192.168.1.99 (the default management address), and sign in with the default admin account to set a new password.
- Run the setup wizard to configure WAN, LAN, DNS and firewall policies, then register the device to activate FortiGuard and FortiCare services.
- Enable security profiles (IPS, antivirus, web filtering, application control), set up SD-WAN and VPN, and upgrade to the recommended FortiOS release.





Reviews
There are no reviews yet.